Turn AI Compliance Requirements Into Operational Controls

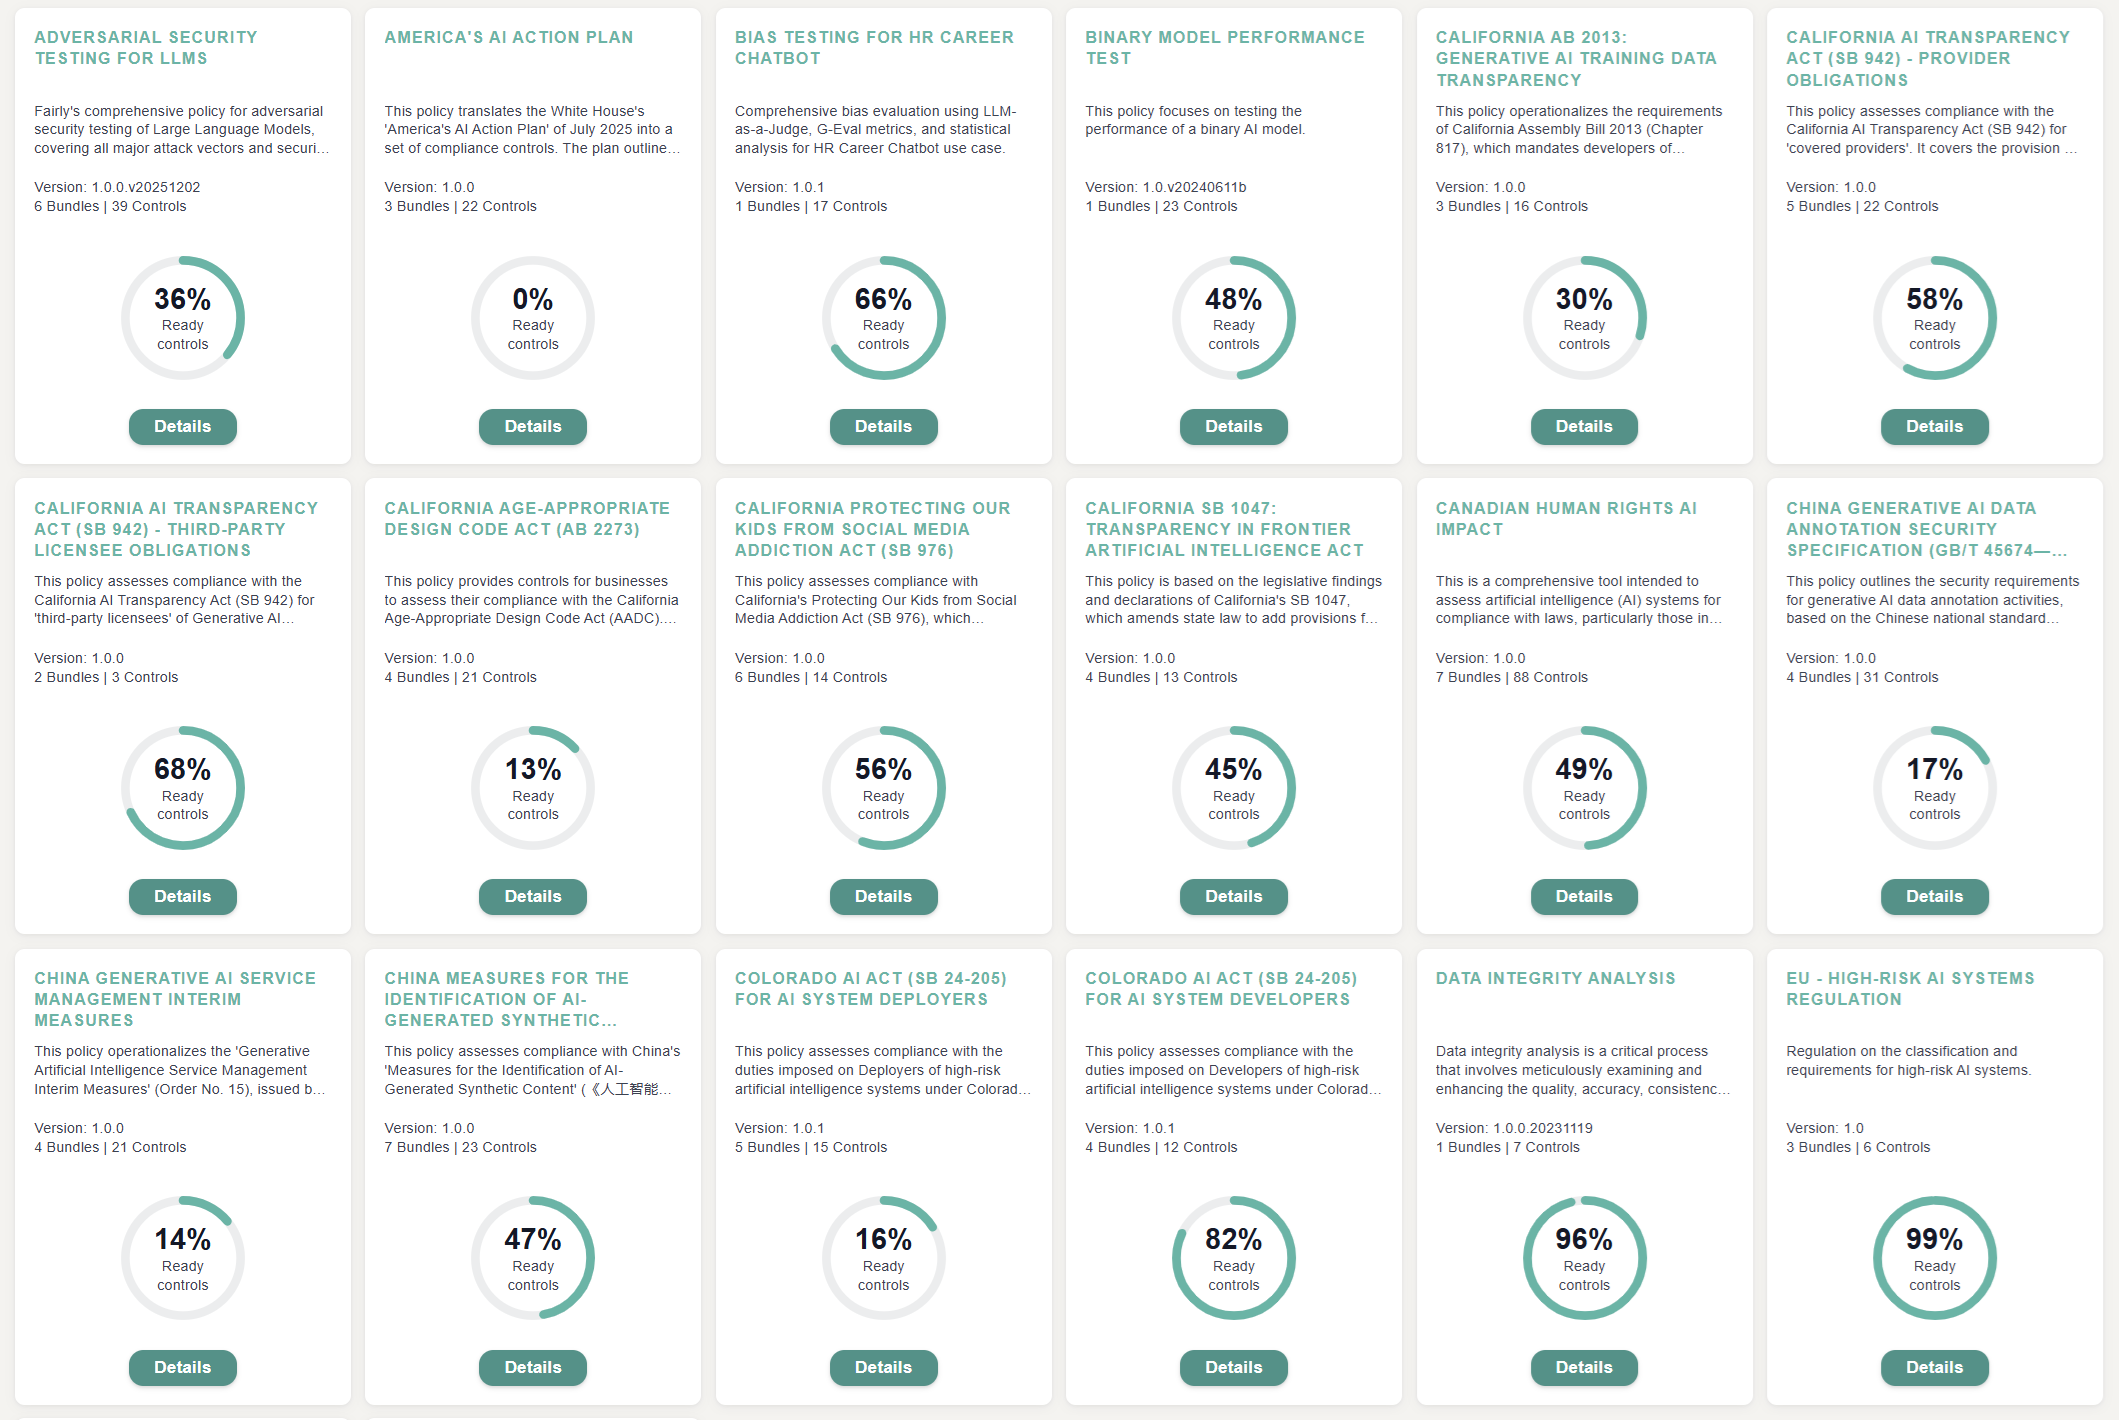
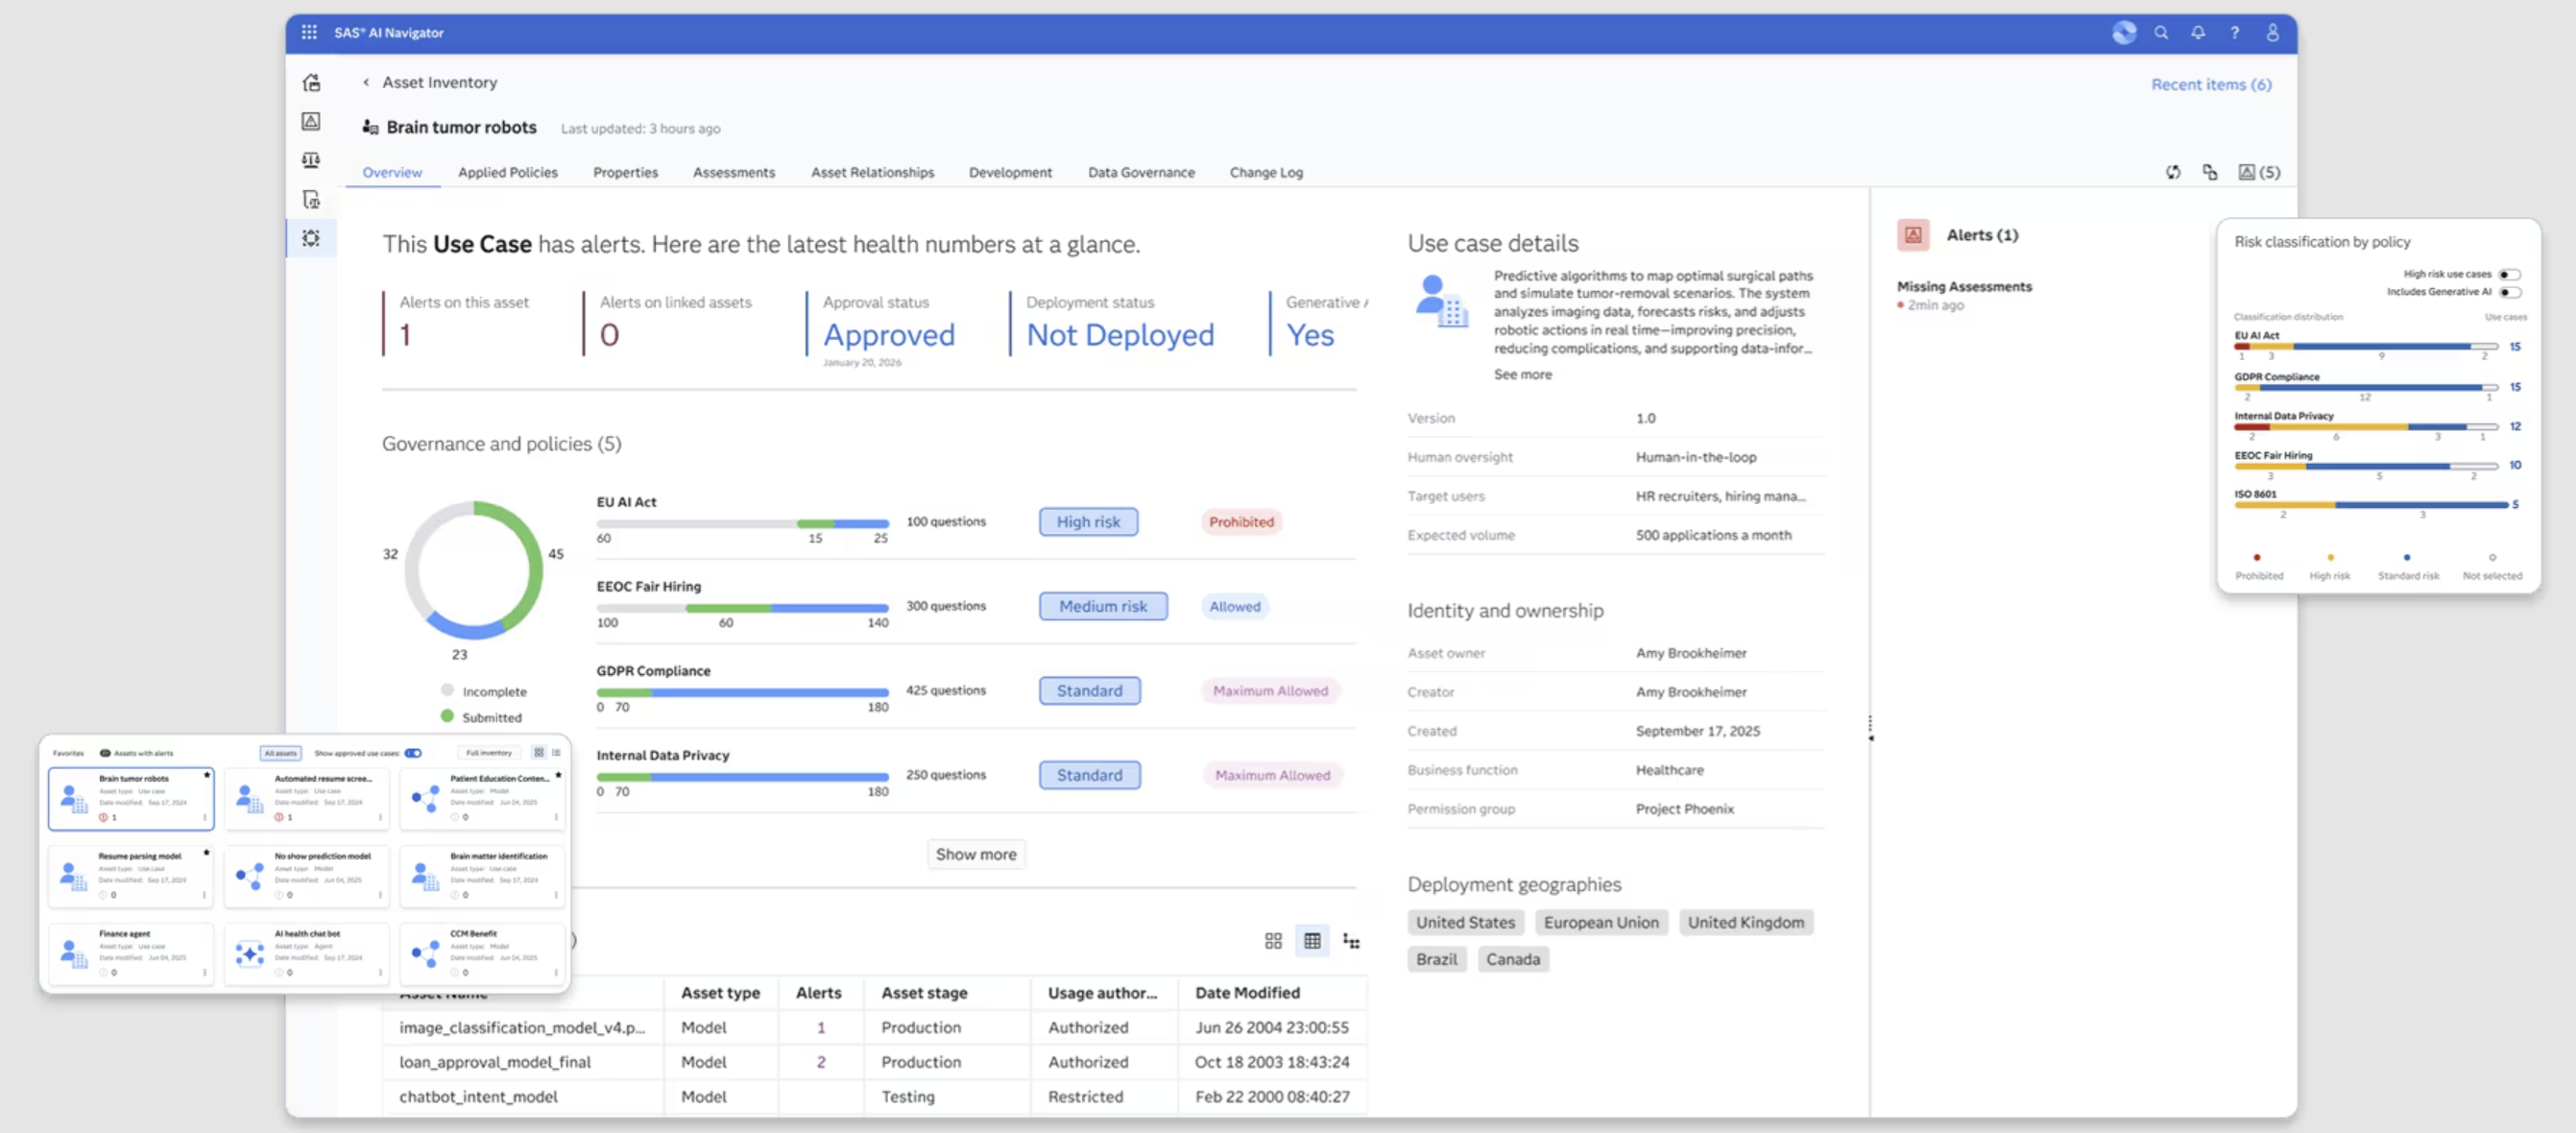
From regulations and standards to internal policies and bespoke requirements, Asenion Policy Packs translates compliance requirements into operational controls that can be applied to any AI use case. Asenion Policy Packs are available for use within SAS® AI Navigator.

Asenion
+

Every Requirement. Every AI Use Case. Operationalized.

AI compliance does not start and end with the EU AI Act, NIST AI RMF or ISO/IEC 42001. Organizations must comply with a growing body of regulations, standards, industry requirements, contractual obligations and internal policies, often across multiple jurisdictions and business functions.

Mobile reports

Asenion Policy Packs translates external requirements (laws, regulations, standards, industry frameworks, customer and contractual obligations) and internal requirements (corporate AI, responsible AI, information security, privacy, model risk and HR policies, or any custom requirement) into machine-readable compliance controls mapped to the AI systems, models, agents and use cases they govern.

Mobile reports
AI System Screening
How it works

From requirements to operational compliance

Every requirement, translated into controls and applied to every AI use case.

01

Source

Regulation, standard, framework, internal policy or custom requirement.

02

Translate

Convert requirements into structured compliance controls and testable criteria.

03

Apply

Ingest policy into SAS AI Navigator and apply controls to specific AI use cases.

04

Test & Verify

Evaluate whether the AI system meets the applicable requirements.

05

Evidence

Create traceable evidence of compliance and control effectiveness.

NIST AI Risk Management Framework

Compliance for any stage of your AI lifecycle.

Daily reports

A single organization may need to apply different requirements to a customer-facing chatbot, an HR screening system, an AI coding agent, a financial model, a healthcare application or an autonomous AI agent. Asenion lets you define what compliance means for each AI use case, combining regulation, standards, industry requirements and internal policies into a single, operational compliance program for your AI lifecycle end-to-end.

Mobile reports
Mobile reports

Better Together

Daily reports

Asenion Policy Packs are available for use within SAS AI Navigator, extending AI compliance beyond predefined regulatory frameworks to the requirements specific to each organization. SAS AI Navigator is where AI is managed; Asenion turns compliance requirements into controls.

Applicable regulations

The requirements that apply in each industry SAS serves

Examples of the regulations, standards and frameworks organizations in each industry may need to apply to their AI. Asenion Policy Packs translate requirements like these into operational controls.

Banking

Model risk and AI requirements such as OSFI E-23, SR 26-2, fair lending (ECOA and Regulation B) and the EU AI Act.

Explore banking AI compliance →

Insurance

Colorado SB21-169, the NAIC Model Bulletin on the use of AI by insurers and the EU AI Act.

Explore insurance AI compliance →

Health Care

HIPAA, the EU AI Act, FDA guidance on AI-enabled medical device software and internal clinical safety policies.

Explore health care AI compliance →

Public Sector

Canada’s Directive on Automated Decision-Making, the EU AI Act and public-sector transparency and accountability requirements.

Explore public sector AI compliance →

Telecom, Media & Technology

The EU AI Act, GDPR, consumer protection rules and AI security frameworks such as the OWASP Top 10 for LLM Applications.

Explore telecom, media & tech AI compliance →

Education

The EU AI Act, which treats many education uses as high-risk, alongside FERPA, GDPR and institutional academic integrity policies.

Explore education AI compliance →

Small & Midsize Business

ISO/IEC 42001, NIST AI RMF and the EU AI Act, scaled for startups and small and midsize teams.

Explore SMB AI compliance →

Life Sciences

Translate ISO/IEC 42001, the EU AI Act, data provenance and internal R&D policies into controls for AI across research and development.

Explore life sciences AI compliance →

Manufacturing

Apply Rolls Royce's Aletheia Framework® and operational risk requirements as controls for AI in production, quality and supply chain.

Explore manufacturing AI compliance →

Retail & Consumer Goods

Consumer protection, privacy (GDPR, CCPA) and fairness requirements for customer-facing AI and chatbots.

Explore retail & CPG AI compliance →

Hospitality

Privacy (GDPR, CCPA), fairness and customer-interaction requirements for guest-facing and generative AI assistants.

Explore hospitality AI compliance →

Oil & Gas

Translate safety, operational risk and internal policies into compliance controls for AI in operations and asset management.

Explore oil & gas AI compliance →

Travel & Transportation

The EU AI Act, GDPR and consumer protection and pricing transparency requirements for AI in customer service, pricing and logistics.

Explore travel & transportation AI compliance →

Utilities

NERC CIP, cybersecurity and operational risk requirements for AI supporting critical infrastructure.

Explore utilities AI compliance →

Legal & LegalTech

Keep AI-assisted research, drafting and e-discovery within Law Society rules, court AI directives and ISO/IEC 42001, with accredited CPD training for lawyers.

Explore Legal →
Why Us

Every requirement. Every Use Case.

Asenion translates regulations, standards, industry requirements and internal policies into operational controls for AI compliance.

Every Requirement

Laws, standards, industry frameworks, contractual obligations and your own internal policies.

Translated Into Controls

Structured, machine-readable compliance controls and testable criteria.

Applied to Every Use Case

Mapped to AI systems, models and agents, with traceable evidence of compliance and control effectiveness.

Want to accelerate safe & compliant AI adoption?

Schedule a call with one of our experts to see how Asenion can help
‍